What I’m wanting to do is allow the user choices and flexibility. A user might want to enable passwordless as a backup to their 2FA, so if they lose their phone (which has the authenticator app), they can still login using passwordless. But given that having 2FA enabled always forces its use, they wouldn’t be able to log into my app if they lose their phone.
Yes, 2FA offers stronger protection than passwordless via email, which itself offers better protection than a password alone, but plenty of apps & sites are perfectly fine with using passwordless alone. I don’t see the point of forcing 2FA on top of passwordless.
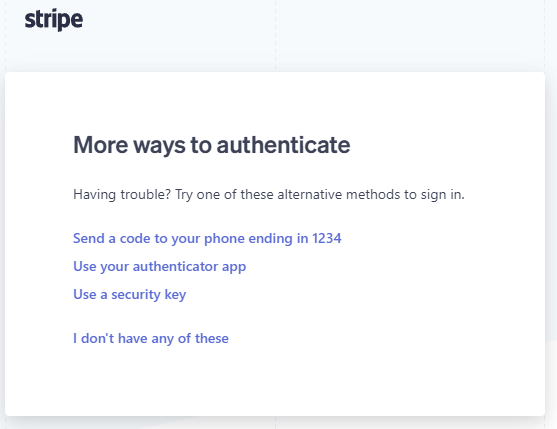
BTW, what I’m trying to setup is exactly how Stripe does its MFA:
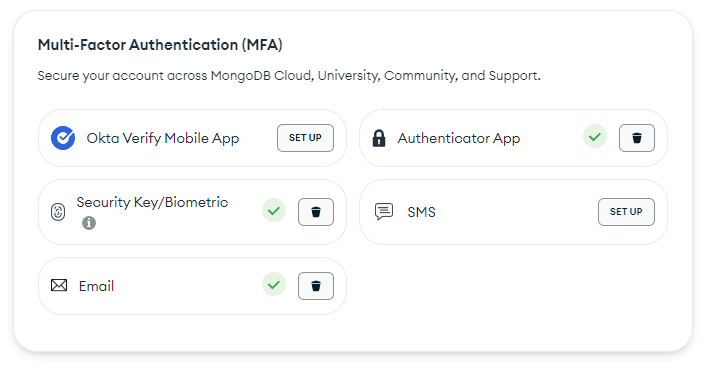
Same for MongoDB Atlas MFA: